


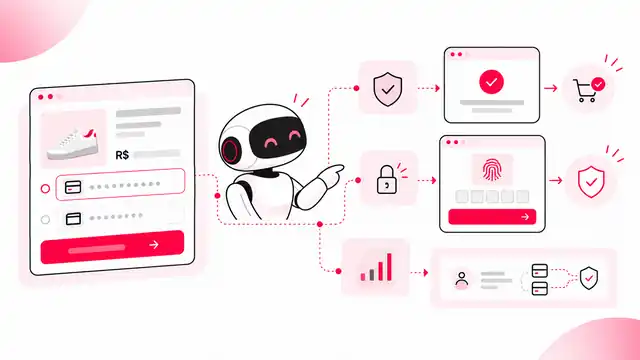
3D Secure is often presented as an extra security step for card purchases. That definition is correct but incomplete. In modern operations, 3DS also influences experience, liability, risk data, approval rates, and integration design.
The discussion goes beyond simply enabling or disabling authentication. The real challenge is deciding when to authenticate, which data to send, how to handle frictionless and challenge flows, how to interpret the result, and how to connect authentication to the rest of the payment infrastructure.
Poorly implemented, 3DS can add friction without a clear benefit. Well integrated, it can increase confidence in the flow and provide more context for authorization and risk decisions.
What is 3D Secure?
3D Secure, or 3DS, is a card payment authentication protocol that creates an additional exchange of information among ecosystem participants before or during authorization.
The modern version of the protocol was designed to enable risk-based authentication, reducing the need for direct cardholder interaction on transactions considered lower risk and triggering additional steps when needed.
In practice, the merchant and its infrastructure send transaction data and purchase context. This data is evaluated within the authentication ecosystem and may result in a flow without a visible challenge or a confirmation step involving the customer.
Is 3DS the same as fraud prevention?
No.
Fraud prevention and 3DS may use risk signals, but serve different roles.
A fraud prevention solution generally assesses the likelihood of a transaction being fraudulent based on models, rules, and merchant or provider context. 3DS is an authentication protocol tied to the card ecosystem and issuer.
The two can coexist.
An operation may analyze risk internally, request 3DS in certain cases, and still use other controls before or after authentication.
AZPay documentation presents fraud prevention, 3DS, and zero-auth as complementary security layers, not substitutes for one another.
What is a frictionless flow?
Frictionless is a flow in which authentication occurs without requiring a noticeable additional interaction from the cardholder.
The system sends enough context for the risk assessment to allow authentication to complete without a challenge.
For the user, the experience may resemble a standard checkout. The difference lies in the data and messages exchanged among the merchant, 3DS infrastructure, card network, and issuer.
This possibility is one reason the quality of submitted data matters so much. The more consistent and complete the context, the better the ecosystem can make a risk-based decision.
What is a challenge?
A challenge is a flow in which the cardholder must complete an additional authentication step.
This step may involve confirmation in a banking app, biometrics, a code, a password, or another method supported by the issuer.
A challenge adds friction because it interrupts the direct checkout sequence. But it exists precisely for situations where the issuer needs greater confidence before authenticating the transaction.
The experience must be treated as part of the product. If the application cannot correctly open, resume, or interpret the challenge, technically valid authentication can turn into abandonment.
Who decides whether there will be a challenge?
The merchant can influence the flow through data, preferences, and permitted rules, but the final decision depends on the 3DS ecosystem and issuer.
This matters because some teams treat 3DS as a deterministic frontend rule: enable it and a screen appears; disable it and no screen appears.
The actual behavior is more dynamic.
The same integration may produce a frictionless flow for one transaction and a challenge for another, depending on risk, context, market, and the issuer's decision.
The application must be ready for both.
What is data-only 3DS?
Data-only is an approach that shares transaction context data to support risk assessment without necessarily executing the full authentication flow with a challenge.
It can be useful in performance and approval strategies when the infrastructure and participants support this model.
AZPay documentation includes a specific Data-Only 3DS integration alongside the full 3DS flow.
This highlights an important distinction: sharing signals and authenticating are not exactly the same thing.
The design should consider the outcome operations need and which capabilities each route offers.
Does 3DS increase approval rates?
It can in some contexts, but there is no universal rule.
Additional authentication can give the issuer more confidence in the cardholder's identity and reduce certain risks. In some scenarios, this may support authorization approval.
At the same time, challenges add friction and can cause abandonment. A poor integration may lose conversion before even reaching authorization.
Measuring approval rate alone is therefore insufficient.
Operations must track the full conversion journey: checkout start, authentication attempt, frictionless or challenge flow, challenge completion, authorization, and completed purchase.
Are security and conversion opposites?
They do not have to be.
The false choice between security and conversion arises when every control is treated as a fixed step applied equally to every transaction.
Risk-based models aim to apply more friction where needed and less where confidence is sufficient.
The goal is not to remove controls to increase conversion. It is to use context so that the level of control is proportional to risk and ecosystem rules.
Mature infrastructure measures the cost of each step without treating security as an unavoidable obstacle.
Which data influences a 3DS flow?
The protocol may use transaction, browser or device, merchant, and cardholder information, depending on the flow and implementation.
Inconsistent, missing, or incorrect data reduces the quality of context reaching participants.
Apparently technical fields such as device information should therefore not be sent merely to fill a schema. They represent signals that may inform the authentication decision.
AZPay documentation includes device_info fields and 3DS-related parameters when creating charges, reinforcing that authentication must be integrated into the full payment context.
What happens after authentication?
3DS does not replace financial authorization.
A transaction may be authenticated and still declined by the issuer because of available funds, a limit, a block, or another rule.
Authentication answers a question about identity and confidence in the context. Authorization answers whether the financial transaction can proceed.
Mixing these states makes diagnosis harder.
The application must know whether authentication failed, the challenge was abandoned, or authentication completed and financial authorization was later denied.
These are different problems requiring different actions.
How does 3DS relate to fraud prevention?
A risk strategy can use fraud prevention to decide when to require stronger authentication, allow a simpler flow, or block a transaction before sending it to the processor.
The specific design depends on the merchant's tools and rules.
The 3DS result may also become an additional signal for later decisions.
What matters is avoiding unclear duplication of responsibilities. If multiple layers make risk decisions without sharing context, the experience can become inconsistent.
A risk architecture needs an explicit order and responsibilities.
What does liability shift mean?
In certain card network and authentication contexts, successful use of 3DS can change liability for certain types of fraud.
This concept is known as liability shift.
The actual rules depend on the network, market, transaction type, and protocol outcome. Liability shift should therefore not be treated as an automatic guarantee whenever 3DS appears in the flow.
For the merchant, the point is that authentication can affect more than immediate approval. It also contributes to the ecosystem's liability model.
Current rules should always be checked against the applicable official sources.
Is 3DS mandatory?
That depends on the market, transaction type, and applicable rules.
Regions with strong authentication requirements may make 3DS especially relevant, while other markets have different dynamics.
There are also exceptions, exemptions, and specific treatments.
A global platform should not assume a single rule applies to every country.
This matters for orchestration: the selected route must support not only the method and currency, but also the authentication requirements for that context.
What changes in a multi-PSP architecture?
In a multi-PSP operation, authentication and processing may be coupled differently depending on the provider.
If a transaction was authenticated in a particular context and the authorization route subsequently changes, the infrastructure must know which data and results remain valid on the new route.
Switching processors after 3DS should not be treated as a simple, context-free retry.
Compatibility among authentication, token, acquirer, and provider must be understood before implementing failover.
This is one reason smart routing should consider capabilities, not just historical performance.
Can 3DS be part of routing?
Yes, as a constraint or signal.
An engine may know that a route supports a specific authentication mode, another provider has different requirements, or a market requires a certain behavior.
This does not mean choosing a route solely to avoid authentication.
It means including authentication in the route capability matrix.
A routing decision that ignores 3DS state may send a transaction down a path unable to complete the flow correctly.
What should you measure in 3DS?
The first metric is the share of transactions sent to 3DS.
Then separate frictionless and challenge flows, challenge completion rate, abandonment, technical failures, successful authentication, declined authentication, and subsequent authorization.
It is also important to compare final conversion across different groups and contexts.
Aggregate metrics can hide problems. A PSP may have good financial approval but poor challenge completion on a particular device. Another may have a higher frictionless share because it receives more complete data.
Observability must cover the entire journey.
How do you diagnose a conversion drop after enabling 3DS?
First, separate authentication from authorization.
Check how many transactions enter a challenge and how many complete it. Analyze whether abandonment concentrates in particular browsers, devices, issuers, or markets.
Then investigate technical failures: callbacks, redirects, lost sessions, timeouts, and integration errors.
Only then compare the financial outcome.
Without this breakdown, it is easy to attribute the entire drop to the protocol when the problem may lie in the challenge implementation.
Embedded checkout and 3DS
Embedded checkout aims to keep customers within the merchant's experience. It does not eliminate external steps needed for authentication.
The product challenge is to integrate these steps without breaking context.
Users need to understand that confirmation is taking place and be able to return to checkout with the correct state.
On mobile, this may involve switching apps. On the web, it may involve components and redirects.
The experience must preserve the order and prevent users from creating a new attempt when they return.
Idempotency still matters
Imagine a customer completes a challenge, but the application times out while resuming the flow.
If checkout immediately creates a new charge, it may cause a duplicate or an unnecessary second authentication.
The infrastructure must correlate the checkout session, authentication, and payment intent.
Idempotency keys, status queries, and asynchronous events help keep that relationship consistent.
3DS adds states; it does not remove the need to control attempts.
Webhooks and 3DS
The charge's final state may continue to evolve after the authentication flow.
Webhooks help synchronize the application with later payment changes.
The merchant should therefore not use the challenge's visual return alone as the final source of financial state.
The experience can tell the user that payment is processing while the infrastructure waits for definitive confirmation.
Separating the interface from financial state prevents incorrect messages.
3DS in recurring payments
The first purchase of a subscription may involve the customer being present and an authentication flow. Future charges may occur in a different operational context.
The infrastructure must correctly represent the stored credential and recurring payment relationship.
This affects how participants understand subsequent transactions.
Trying to execute every recurring charge as a new interactive purchase can create friction or conflict with the business model.
Recurring payments require the relationship to be established correctly from the first payment.
3DS and network tokens
Tokenization and authentication are separate layers, but can work together.
Network tokens represent credentials within card network ecosystems and can carry their own dynamic security elements. 3DS authenticates the purchase context.
An advanced operation may use both according to route and market capabilities.
AZPay documentation maintains separate content for 3DS, Data-Only, and Network Token, helping show that each mechanism solves a different part of the problem.
When not to force a challenge
Forcing unnecessary friction can worsen the experience.
When the protocol and rules permit risk-based assessment, the goal should be to provide enough context for authentication proportional to the transaction.
This does not mean looking for security shortcuts.
It means using the modern 3DS design rather than reproducing a fixed-authentication mindset for every purchase.
The best experience stays secure without asking users to take unnecessary actions.
What does AZPay support in this area?
AZPay documentation includes 3DS for card charges, the full authentication flow, Data-Only 3DS, device information, and integration with other security capabilities such as fraud prevention and zero-auth.
This allows authentication to become part of the payment infrastructure rather than an isolated checkout component.
For merchants, the architectural benefit lies in observing 3DS alongside authorization, approval rates, risk, and routing.
How do you implement it without losing control of the experience?
Start by treating 3DS as a state machine, not a popup.
The application must know when authentication started, when it requires a challenge, when it completed, when it failed, and when payment can proceed.
Preserve identifiers across these stages. Ensure retries do not create new business intents. Keep order state independent of the visual component. Monitor every transition.
Above all, do not hide everything inside one approval metric.
3DS is trust infrastructure
The value of 3DS is not adding another screen to checkout. It is creating a structured exchange of signals and authentication within the card ecosystem.
This can influence security, liability, experience, and authorization decisions.
To realize that value, the company must integrate the protocol into the rest of the architecture: fraud prevention, tokenization, recurring payments, routing, observability, and payment state.
Treated this way, 3DS stops being an isolated obligation and becomes a trust layer within broader payment infrastructure.